Information is a vital asset that underpins the DTS Group's business activities and the trust it earns from its customers. Under its Information Security Basic Policy, the DTS Group works in cooperation with its group companies and business partners to ensure the proper management of information assets. In addition to preventative measures such as establishing management systems and providing education and training, the group promotes consistent information security management, from rapid response to security incidents to preventing recurrence.
basic way of thinking
DTS has established an information security basic policy to protect its valuable information assets and to earn the trust of all stakeholders, including its customers.
Information security promotion system
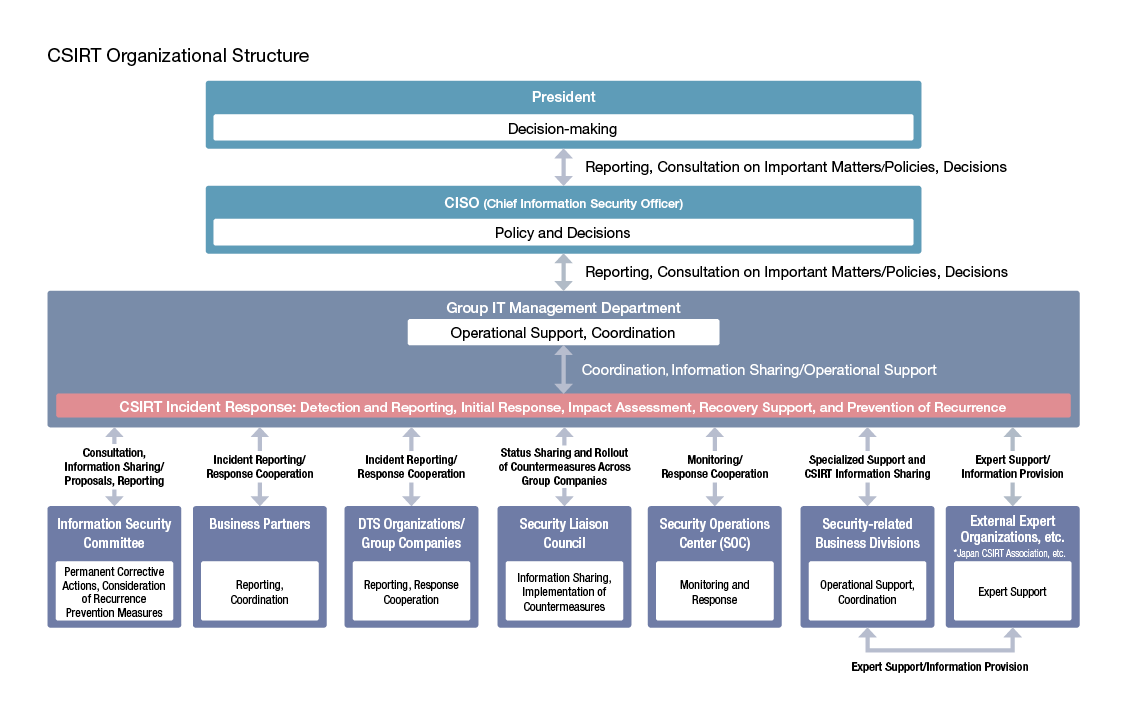
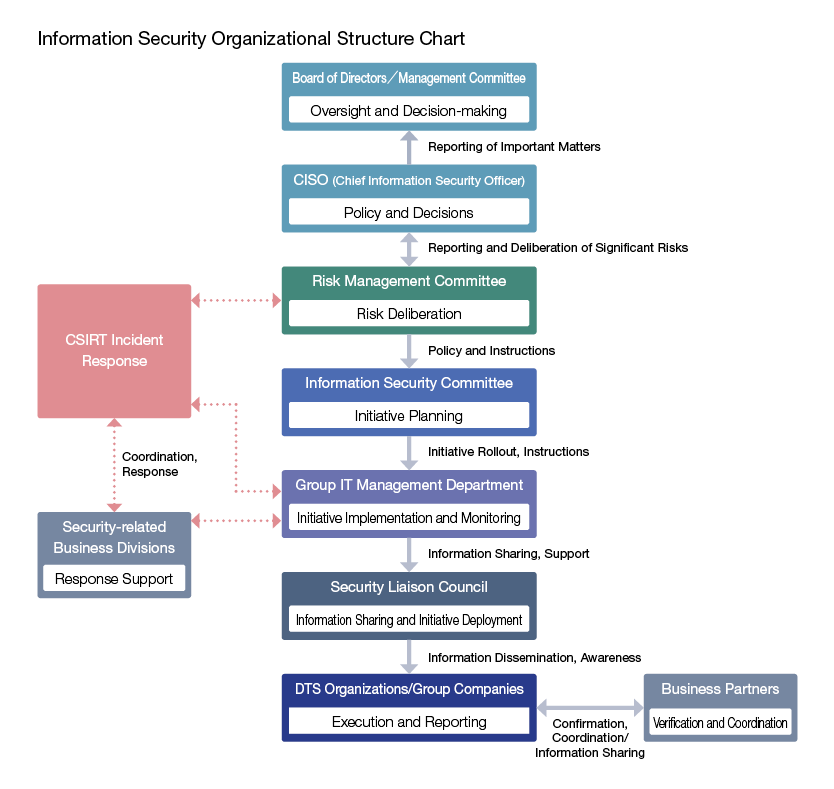
Under the leadership of our CISO, our Group IT Management Department, in collaboration with various organizations and group companies, promotes information security management. Furthermore, we have established a CSIRT (Computer Security Incident Response Team) to handle security incidents, creating a cross-organizational response system both during normal times and in the event of an incident.
- Overall management and promotion
Under the CISO, the Group IT Management Department is responsible for promoting information security measures and monitoring their implementation status.
- Consideration/information sharing
The Risk Management Committee, Information Security Committee, and Security Liaison Committee will deliberate on risks, consider countermeasures, and share information within the group, each based on their respective roles.
- Execution and collaboration
Each organization and group company within DTS implements the measures, and shares information and makes necessary confirmations with business partners as needed, depending on the nature of the work.
Initiatives in daily work
At our company, we integrate information security policies and rules into our daily operations and strive to improve the effectiveness of information security through education and training, monitoring of implementation status, and management during outsourced work.
- Management including group business partners
We distribute information security policies and rules to each organization and group company and continuously monitor their implementation. We also share necessary information and rules with our business partners involved in our operations, ensuring appropriate information management and working to improve information security levels throughout the entire supply chain.
- Education and awareness
We provide ongoing education and awareness training to executives, employees, and business partners involved in DTS projects, covering topics such as the importance of information security, information management in daily operations, understanding security risks arising from the supply chain, the responses required from both the client's and contractor's perspectives, and responses to cyberattacks and incidents.
- Confirmation when outsourcing work
Depending on the nature of the work, the information handled, and the work environment, we confirm the necessary information security management through contracts, checklists, etc. Furthermore, when outsourcing tasks involving personal information, we stipulate the necessary security management measures based on contracts, etc.
Information security management in supply chain management can be found here.
Management tailored to the characteristics of information and services
At our company, we manage our operations based on various management systems and standards, depending on the characteristics of the information we handle and the services we provide. Details regarding the scope of certification/compliance, registered organizations, applicable standards, etc., can be found on the respective pages.

- Information Assets (ISMS/ISMS Cloud Security)
We properly manage the information assets entrusted to us by our customers, implementing preventative measures, providing education and training, responding to problems when they occur, and continuously improving our processes.
Information Security Management System (ISMS)(Japanese only)
- Personal information protection / Privacy Mark
To ensure the proper handling of personal information, we are committed to continuous improvement in areas such as acquisition, use, provision, security management, management of subcontractors, and handling of complaints and inquiries.
Personal Information Protection Management System (Privacy Mark)

- IT Service Management System (ITSMS)
To ensure the stable provision of IT services, we are committed to continuously maintaining and improving service quality while paying close attention to the appropriate management and protection of information assets.
IT Service Management System (ITSMS)(Japanese only)
- Card Information
In our BPO operations that handle credit card information, we implement security management in accordance with PCI DSS.
Incident preparedness and response
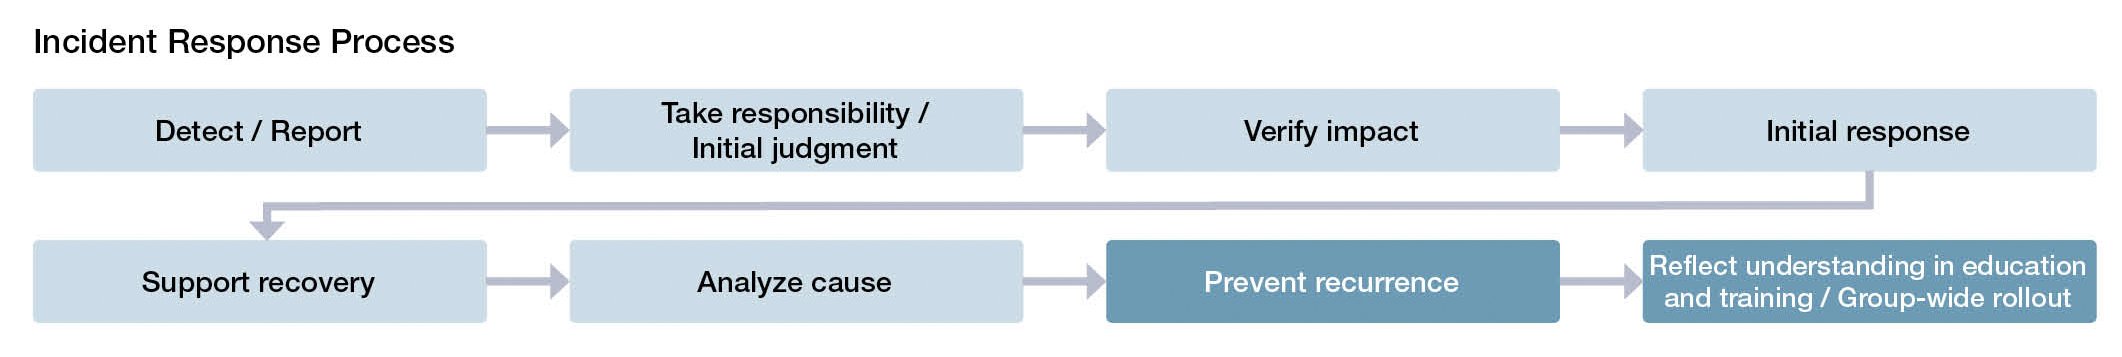
The DTS Group is committed to preventing security incidents and detecting them early. When an incident occurs, relevant departments, primarily the CSIRT (Computer Security Incident Response Team), collaborate to minimize the impact and ensure a swift recovery. Furthermore, the causes and responses are reviewed to prevent recurrence and facilitate continuous improvement.
- Peacetime preparations
We collect threat and vulnerability information to assess its impact on our systems and services. We issue alerts to relevant departments as needed and work to prevent incidents and detect them early through vulnerability assessments of our website and other systems.
- Response in case of an incident
We will assess the scope and severity of reported and detected incidents, and work with relevant departments to develop initial response measures, recovery support, and preventative measures. We will promptly share this information with the CISO and relevant departments as needed to minimize the impact on business operations and customers. Furthermore, if permanent solutions or preventative measures are required, we will collaborate with the Information Security Committee and other relevant bodies to develop internal countermeasures.
- Prevention and improvement of recurrence
We will identify the cause of the incident and the challenges in responding to it, and then formulate measures to prevent recurrence. The knowledge gained will be reflected in the review of education and training, response procedures, and operational rules, leading to an improvement in the information security level across the entire group. Furthermore, if it is necessary to share information and deploy countermeasures to other group companies, we will work to prevent similar incidents from occurring through security liaison meetings and other means.
Incident response system centered on CSIRT
With the CISO and the Group IT Management Department at the core, DTS has established a system for responding to incidents through collaboration among its various organizations, group companies, business partners, and external expert organizations, each fulfilling their respective roles.